> Google dismantles botnet secretly running on 1.3 million Android TV boxes
[AUTHOR: Ryan Whitwam]
[DATE: 03/11/2026 17:08]
[LANGUAGE: EN]
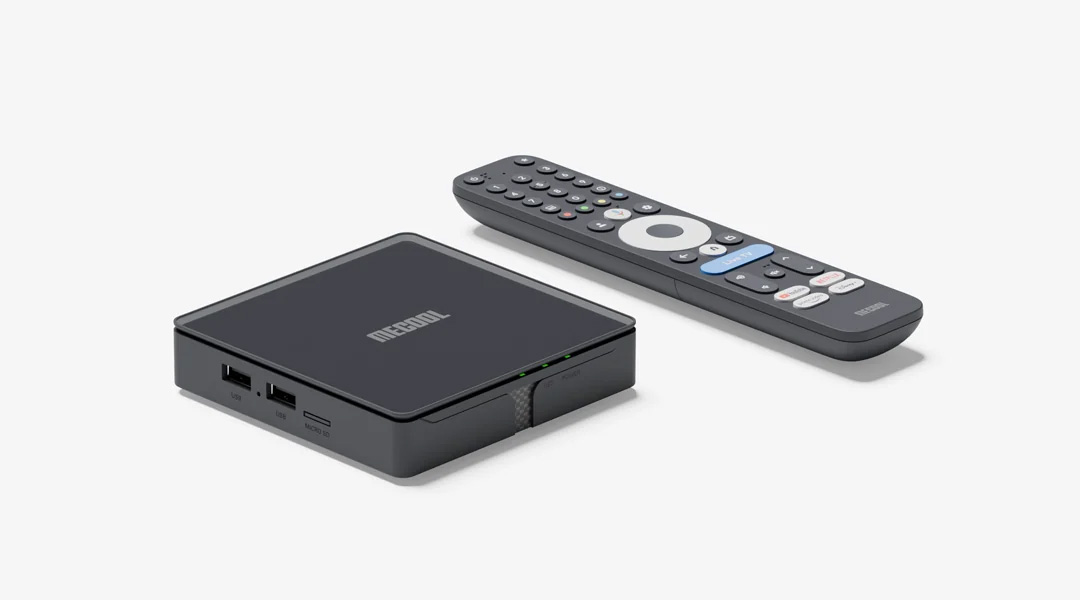
Google's Threat Intelligence Group says it has shut down a massive botnet called x.cpe. At its height, x.cpe ran on more than 1.3 million Android TV devices, and unusually, these were Google-certified boxes. Google says its screening process missed the malware due to "obfuscation techniques" employed by Shenzhen-based Videostrong Technology.
In a detailed blog post, the Threat Intelligence Group explains how the x.cpe botnet evolved quickly from a single-stage dropper into a modular three-stage malware platform that sold access to third parties. Manufacturers must have their devices certified if they want access to Google apps and branding, a process that is supposed to catch threats like this. However, Videostrong's compromised boxes, mostly sold under the MECOOL brand, evaded detection by using a backdoor to remotely install the malware after the devices were set up and online.
After devices appeared online, a stub application called x.cpe or com.oemservice would phone home. This package did not have any malicious capabilities of its own, but it had the system-level permissions necessary to install malware modules at the operator's behest. It also disabled Play Protect, which would have otherwise flagged the silently installed packages as malicious.Read full article
Comments