> Cybercrims go beyond stealing data to attack physical building systems
[DATE: 17/10/2026 11:30]
[LANGUAGE: EN]
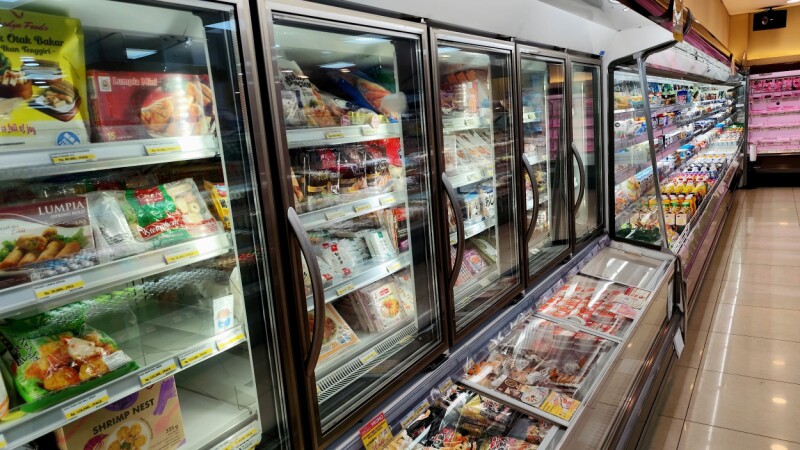
Late Sunday night, a still-unknown cybercriminal or group hacked thousands of remote-controlled refrigeration systems across hundreds of French grocery stores, spiking temperatures, spoiling food, and sparking fires. This is part of an ongoing trend of attacking physical systems that can do damage in the real world. In August, a ransomware attack disrupted building-management systems at a Canadian hospital, affecting door access controls, central HVAC monitoring, and the issuing of staff access cards. And three years ago, cyberattacks hit Las Vegas casinos, causing slot machines to go dark, preventing payment kiosks and ATMs from spitting out cash, and locking guests out of their rooms when the electronic keys stopped working. Not all digital intrusions remain in cyberspace, and attackers don’t need to encrypt files and steal data to cause chaos. Hitting physical systems often produces more severe consequences - and turns up the heat on executives to pay an extortion demand. “There was one gig where the customer was refusing to pay, and so the threat actor was like, ‘Hold my beer, have fun getting into your offices,’ and locked everybody out,” Tim Beasley, a senior incident response consultant at Semperis, told The Register. Beasley won’t name the customer, or provide any incriminating information, but said the incident response involved police smashing glass in addition to his team recovering compromised data. “The cops had to break in, and literally get into the building, breaking some windows, so the customer was able to finally get back in,” he said. We asked if the customer paid the ransom demand, and Beasley yelled: “Oh, hell, no!” A report published earlier this month by ServiceNow’s Armis Labs found increasing evidence of ransomware attackers using physical consequences as leverage in their intrusions. “Today’s BAS operate at the intersection of IT and OT worlds, creating unprecedented exposure,” the report said. Ransomware with physical consequences Building automation systems - BAS - are the critical systems that control and monitor facilities’ HVAC, lighting, energy usage, and water consumption. They also oversee badge readers, door locks, surveillance cameras, fire alarm control panels, and other physical safety equipment. As such, BAS make very attractive targets for ransomware operators looking for high-pressure ways to extort organizations into paying multi-million ransom demands. These systems also appeal to government-backed goons and hacktivists looking to ensure maximum psychological and physical impact during destructive cyberattacks. Armis Labs found 73 percent of organizations own BAS that have been used in ransomware attacks, and this same percentage have known exploited vulnerabilities in at least one of their building automation systems. Additionally, 91 percent of BAS communicate over insecure protocols - opening up an even bigger attack surface for cyber-miscreants wanting to cause physical harm. “The primary thing that we see with any attack on building management systems or physical systems: It’s a great place for the threat actor to hide,” Michael Freeman, ServiceNow’s senior director of threat research, told The Register. “It's easier for them to compromise, and it's easier for them to hide in.” BAS and operational technology (OT) in general have fewer security controls than IT systems. Most require continual uptime, which makes them harder to patch or even scan for vulnerabilities and misconfigurations as this may lead to outages. “One case in particular, against a very large financial institution, the threat actors were staying low and quiet by attacking their BMS systems, and then pivoting into the IT environment,” Freeman said. The intruders were routinely caught - and booted from - the financial institution’s IT systems, so they built backdoors into the BMS to ensure persistent access to both OT and IT networks. “We're also seeing threat actors using AI to understand more building automation systems, especially ones that are using obscure OSs like VxWorks, older Unix-type systems,” Freeman said. AI has entered the chat As multiple security experts have told us in previous interviews, security through obscurity is dead. Not only does AI make it easier for attackers to find bugs – some very obscure and decades old - but it also means criminals no longer need to be OT experts to carry out destructive cyberattacks on critical networks and facilities. Instead, they can use AI to learn all about the obscure protocols and proprietary hardware and software that historically made industrial control systems black boxes. “It’s easier to understand what the controls are,” Freeman said, using the example of an attacker trying to take down a plane, or some similar catastrophic cyberattack. Historically, even advanced, government-backed hacking squads would “be quiet, because you don't know what changing certain settings is going to do,” Freeman explained. “Now you can use AI to say, ‘If I compromise a weight and balance system for airlines, all I need to do now is move this number here to this number, and I just told the system to load heavy stuff on the right side of the plane instead of equal distribution.'” Freeman told us he has seen attackers break into airlines’ OT gear in the past. “But they didn’t know what they were getting into, and so they left them alone,” he said. “Those do cause me concern because in the past I've helped to kick people out of those types of systems.” Industrial orgs increasingly under attack OT security provider Dragos tracks ransomware groups’ claims against industrial organizations on the criminals’ leak sites, along with publicly disclosed intrusions affecting manufacturing and other critical sectors. To be clear: claims on leak sites aren’t always accurate or even true, and the claim itself doesn’t mean operations or control systems were hit. Since 2022, however, “the numbers have been consistently increasing,” Lexie Mooney, senior threat analyst at Dragos, told The Register. The cybersecurity firm tracked 995 ransomware attacks against industrial orgs in 2023, a 49.5 percent increase from 2022. That number jumped more than 87 percent in 2024. Active ransomware groups targeting industrial orgs also grew in 2024 to 80 groups, up from 50 the year before. Dragos tracked 119 ransomware groups impacting more than 3,300 industrial organizations in 2025, and the incidents have steadily increased every quarter this year: 1,020 incidents in the first quarter of 2026 and 1,140 incidents in Q2. “The vast majority of cases are opportunistic,” Abdul Alamri, a senior threat analyst at Dragos, told us. “In some of the cases that we have seen an operational impact, either physical systems or an OT operation, it’s just the nature of the opportunism on the part of those ransomware groups.” This is partially due to the complexity of OT systems, he added. “Ransomware groups want to disrupt operations, and put pressure on the victims to pay the ransom,” Alamri said. “They don’t want to invest that time and effort to target complex systems." It’s usually quicker and easier for financially motivated crims to affect operations via IT systems - as the extortionists did in the August 2025 Jaguar Land Rover (JLR) breach, which halted manufacturing and crippled business operations for months. Internet-connected OT: the next 'low-hanging fruit' The other side of this complexity, however, is that many organizations themselves still lack visibility into their OT environments. Dragos estimates that fewer than 10 percent of OT networks worldwide currently have sufficient network monitoring in place. Plus, in 30 percent of incidents the security firm responded to in 2025, the investigations did not begin with a detection alert, but with someone noticing that “something seemed wrong” in operations. This lack of visibility, combined with threats from AI, worries Alamri. “If you compare the risk that we have seen from humans, to what we are about to face in the near future with AI agents who might continuously try to break into those systems - it’s a pretty dark future if we don't take the right measures to protect ourselves against it.” As organizations get better at patching and securing IT systems, attackers will likely look to internet-connected OT systems where digital compromises have real-world consequences, according to Matt Hayden, VP of cyber and emerging threats at General Dynamics Information Technology. “We all anticipate that as we get better at reducing the IT low-hanging fruit, OT will become a vector of much more scrutiny and much more attention,” Hayden told The Register. Before joining GDIT, Hayden served as the assistant secretary for cyber, infrastructure, risk and resilience policy at the US Department of Homeland Security. Compliance vs. security “There is a big focus on the hardware being connected for the purpose of compliance - and to make sure that, in the name of compliance, we aren't opening back doors, to devices that traditionally wouldn't have to be connected to facilitate their service,” he said, using refrigeration units as an example of one such system that is now internet-connected for compliance purposes. This was prior to the French supermarket hacks. Refrigeration units’ monitoring systems connect to the internet so their owners and operators can prove to regulators that the units maintain their uptime and temperature in accordance with regulations. “So if the health department comes by, they say, ‘Look, my refrigerator was at 27 degrees for the last 72 days,' and they have a check mark, and they get their A plus. But that simple connectivity is also a vector in which that particular refrigerant unit could be targeted for disruption,” Hayden said. About a week after our interview, criminals did exactly that. “The recently reported exploitations of commercial refrigeration units represent a significant example of devices without digital value, no sensitive data or extended enterprise access, being exploited by being connected to the internet with unpatched firmware,” Hayden told us in a subsequent email. He said he expects the attribution to be “less nation-state, and more likely those looking for targets of opportunity to identify what could be done with the unpatched systems.” “The consequences are food supply degradation at a small scale, but it is an important example of what could happen at scale very quickly with more consequential operating equipment,” Hayden said.®